Advisory · Buenos Aires · Since 2023
NoHypeEngineering
Technical advisory on cybersecurity and software engineering, for boards, risk committees and executive teams.
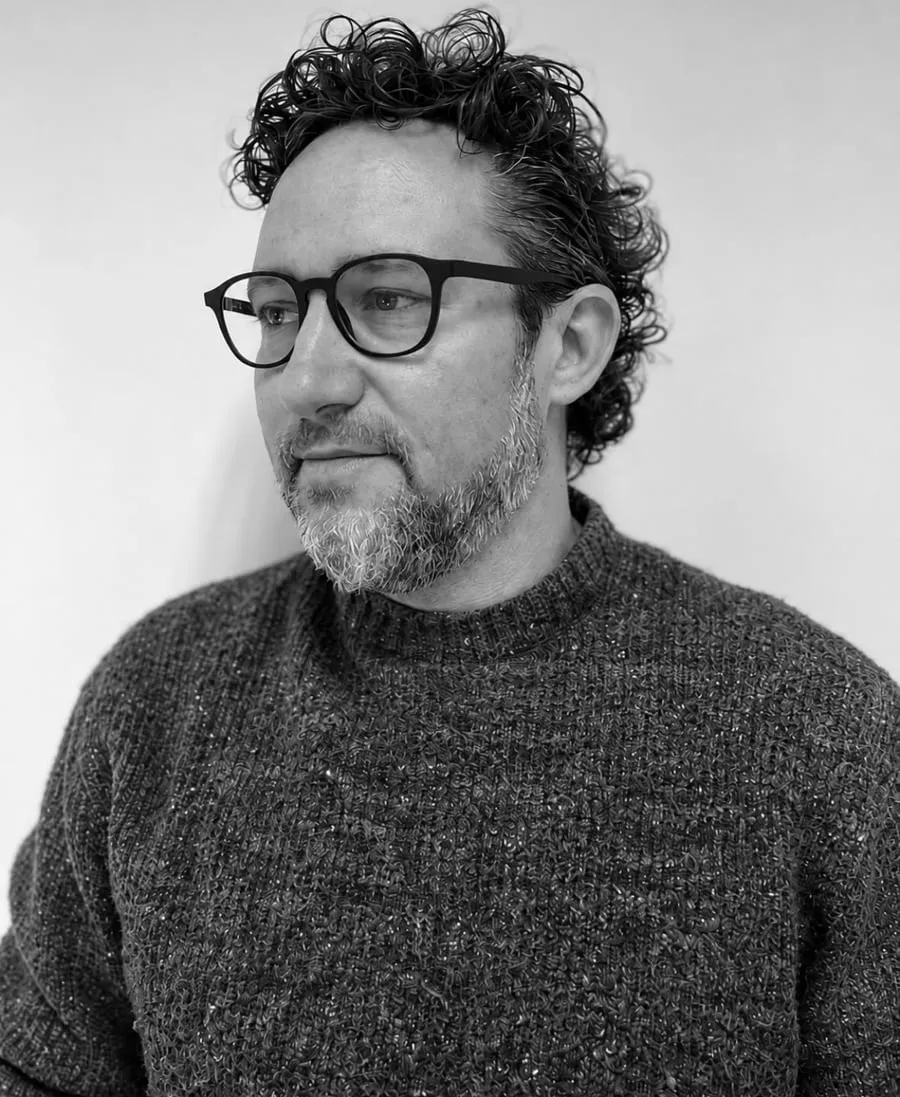
Led by Ezequiel Gutesman
NoHype Engineering advises boards, CEOs, CIOs and CISOs of large organizations on governing cyber risk and, building on that, on running engineering at scale. Its director spent ten years at Onapsis — which secures business-critical SAP and ERP applications — first building its security research team and then leading engineering and research together; before that, seven years as a security researcher at CORE Security Technologies; and most recently he was Executive Deputy Director of Argentina's National Cybersecurity Center, during its creation.
Organizations the firm has worked with
Some advised from the outside; others where its director worked, as part of the team.

Two practices, and one of the two problems lives inside the other
The main practice is cybersecurity. The second is software engineering, and it is not there to round out a catalogue: much of a large organization's risk is not fixed by buying one more tool, but by changing how its teams build and operate software. That is why the firm does both, in that order.
Cybersecurity for boards and executive teams
So leadership understands its cybersecurity risk in business terms and can decide where to invest.
- Cyber-risk governance and board reporting
- Maturity assessment and a prioritized investment roadmap
- Security architecture and reducing the exposure surface
- Regulatory and critical-infrastructure readiness
- Incident readiness, with exercises alongside leadership
Engineering transformation
Changing how a large engineering organization delivers software, with security built into the process rather than bolted on at the end.
- Delivery and DevSecOps at scale, measured with DORA and SPACE for leadership
- Designing large engineering organizations
- Architecture and platform modernization, with a technical-debt plan
- Professionalizing research and innovation teams
The conversation usually starts with the technical team
The mandate belongs to leadership, but the first call rarely comes from there: it comes from a CTO, a head of engineering or a CISO who already knows where the problem is and needs someone to put it, in the right terms, on the table where decisions are made. The firm works with that person from the start and all the way through.
It starts with whoever sees the problem
A technical conversation, no sales pitch, with the people who live with the system every day.
It reaches the table where decisions are made
The same diagnosis, translated into impact on operations, revenue and regulation, so the board can weigh it against its other priorities.
It comes back to the team as a plan
The decision returns with who does what, in what order and how it is measured. A recommendation that stays in the deck changed nothing.
Four ways to work together
The format depends on the decision the organization has to make, and on how much of that decision is already made.
Ongoing advisor
A standing advisory role to the board, a risk committee or the executive team, with regular sessions and availability for critical decisions.
DeliverablePeriodic risk briefings and a written record of recommendations.
Focused assessment
A four- to eight-week review of cybersecurity posture or engineering practice, based on interviews and on documents and data from the organization.
DeliverableA written report with findings and a prioritized roadmap.
Transformation support
Working alongside the internal team through a security or engineering transformation program over several months.
DeliverableProgram governance, progress metrics and a handover to internal leaders.
Technical support for the team
Working alongside the team that executes — architecture, application security, delivery practices — once the decision is made and what is left is carrying it out.
DeliverableDocumented technical decisions and internal leaders who can sustain them.
What "no hype" means in practice
- Risk in business termsFindings are expressed as impact on operations, revenue and regulation, so leadership can weigh them against other priorities.
- Measure firstRecommendations start from the organization's own data: incidents, audit results and delivery metrics.
- Proven technologyTools and frameworks are chosen for the specific problem the organization has.
- Security inside engineeringSecurity belongs in design reviews, pipelines and the definition of done.
- Written decisionsRecommendations and decisions are recorded with their context, so the next team can follow the reasoning.
Twenty years in industry and government
This is where what the firm offers comes from: the roles, the years and the teams its director led, in product companies and in government.
- 2026
Executive Deputy Director
Centro Nacional de Ciberseguridad (Argentina)
Worked on the creation of Argentina's National Cybersecurity Center. Technical direction and leadership of the governance group. Worked on the definition of critical information infrastructure, the regulatory framework and the technical capabilities of national public-sector agencies.
- 2023 —
Fractional CTO · VP of Engineering · Tech coach
NoHype Engineering
Working with engineering leaders in high-growth companies on SDLC practices, team building, architecture and due diligence.
- 2017 – 2023
VP of Engineering & Security Research
Onapsis
Responsible for the flagship product and for security research. Software architecture, SDLC, QA, support, product security, penetration testing teams and leadership coaching.
- 2012 – 2017
Director of Research
Onapsis
Built the security research team from scratch. Led product innovation, prototypes, patents, conference publications and penetration testing services.
- 2005 – 2012
Security Researcher
CORE Security Technologies
Research on new attack vectors in web applications, wireless networks and other technologies, and penetration testing. Co-inventor of three of the patents listed below and speaker at Black Hat USA, Hack.lu, FIRST and PyCon Argentina, among others.
- 2004 – 2005
Developer
Digbang!
Web development in PHP, .NET and Perl.
- 2001 – 2012
Programming professor · Director of Special Projects in Computing
Escuela Técnica ORT
Taught software programming, directed special projects in computing and advised on the computer science curriculum.
Teaching
Information Security module, Master in Management + Analytics (MIND)Universidad de San Andrés · 2017–2020
Programming teacher and director of special projects, Computing specialtyEscuela Técnica ORT · 2001–2012
Community
Speaker in 2013; later on the content committee, selecting talks for the conferenceEkoparty · 2020–2024
Education
Computer ScienceUniversidad de Buenos Aires
Engineering Leadership for Emerging LeadersMIT Professional Education · 2017
Computing technician, cum laudeEscuela Técnica ORT · 2000
Talks, papers and patents
Most of this work comes from CoreLabs and Onapsis Research, done with colleagues listed as co-authors.
| Year | Venue | Title |
|---|---|---|
| 2014 | NoSuchCon, Paris | Blended Web and Database Attacks on Real-time, In-Memory Platforms |
| 2013 | Ekoparty, Buenos Aires | ERP Security: How Hackers Can Open the Safe and Take the Jewelswith Jordan Santasieri |
| 2012 | PyCon Argentina | No toca BOTOn: Amazon Web Services desde Pythonwith Fernando Russ |
| 2011 | Hack.lu | Abusing the Windows WiFi Native API to Create a Covert Channelwith Andrés Blanco |
| 2009 | FIRST, Santiago | Attacker-centric risk assessment and metricswith Fernando Miranda |
| 2008 | Hack.lu | gFuzz: An Instrumented Web Application Fuzzing Environment |
| 2007 | Black Hat USA | A Dynamic Technique for Enhancing the Security and Privacy of Web Applicationswith Ariel Waissbein and Ariel Futoransky |
| Year | Venue | Title |
|---|---|---|
| 2011 | Hack.lu | Abusing the Windows WiFi Native API to Create a Covert Channelwith Andrés Blanco |
| 2010 | ACM CSIIRW | The impact of predicting attacker tools in security risk assessmentswith Ariel Waissbein · doi:10.1145/1852666.1852752 |
| 2008 | Hack.lu | gFuzz: An Instrumented Web Application Fuzzing Environment |
| 2007 | Black Hat USA | A Dynamic Technique for Enhancing the Security and Privacy of Web Applicationswith Ariel Futoransky and Ariel Waissbein |
| Number | Year | Title |
|---|---|---|
| US 10,257,228 | 2019 | Real-time detection and prevention of segregation of duties violations in business-critical applicationsOnapsis |
| US 9,923,917 | 2018 | Automatic calculation of cyber-risk in business-critical applicationsOnapsis |
| US 9,183,397 | 2015 | Automated computer security compromise as a serviceCore Security |
| US 8,146,135 | 2012 | Establishing and enforcing security and privacy policies in web-based applications (continuation)Core Security |
| US 7,831,995 | 2010 | Establishing and enforcing security and privacy policies in web-based applicationsCore Security |